

Leveraging the Splunk platform to enhance Cisco Identity Services Engine information
Cisco Identity Services Engine (ISE) unifies identity, visibility, and enforcement so teams can verify trust, segment access, and contain threats across hybrid networks. It helps network administrators with all the following security configurations:
- Centralized authentication, authorization, and accounting
- Device profiling and posture assessment
- Guest management and TrustSec segmentation
ISE is a robust platform that includes its own alerting and reporting capabilities. Establishing a standardized operational workflow and consolidating data in a centralized location facilitates efficient troubleshooting and enables seamless data sharing among users. To enhance monitoring and management across diverse ISE deployments, Cisco IT leverages the Splunk platform as an interface. This integration allows for the creation of comprehensive monitoring solutions tailored to support various deployment scenarios effectively.
This article explains how to get started with this integration.
Prerequisites
Before you begin, configure collection of ISE syslog data by using:
- Splunk Add-on for Cisco Identity Services (Documentation available on the Cisco Community)
- Cisco Enterprise Networking for Splunk Platform
Use cases for this integration
This article covers two use cases for the integration of ISE with the Splunk platform.
- Alerting for authentication or performance deviations
- Real-time ISE traffic analysis, deployment health monitoring, and migration activity tracking
Alerting for authentication or performance deviations
Outcomes of this use case:
- Detect anomalies in authentication patterns, including excessive authentication attempts, unusual login times, and unexpected device types, by establishing behavioral baselines for users and devices.
- Trigger timely alerts to security teams upon detection of deviations from normal authentication behavior to enable rapid investigation and response, minimizing potential security risks.
- Monitor system performance metrics continuously and generate alerts when deviations from normal performance behavior occur, facilitating prompt identification and resolution of performance-related issues.
- Implement mechanisms to detect and alert on configuration changes within the environment, supporting auditing processes and ensuring compliance with security policies.
- Integrate these alerting capabilities into a centralized monitoring platform to provide security teams with real-time visibility and actionable insights for effective threat detection, auditing, and compliance management.
Build a basic alert in the Splunk platform
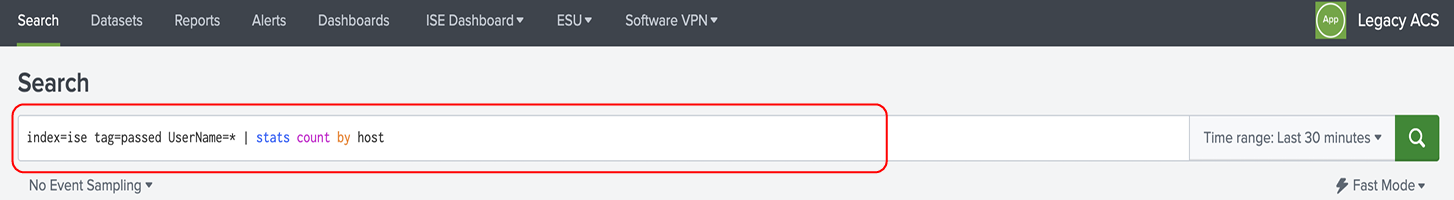
- Construct a query that will capture what you want to alert on. If you need help with Search Processing Language (SPL), you can use the Search Reference or the Splunk AI Assistant for help. The following is a simple example of a search.
- Save the search as an Alert.
- Assign the alert parameters. For more information on alert configuration, see Getting started with alerts.
The alerts you create can be critical or informational.
Critical alert example flow
Critical alerts will vary based on your environment, but some examples are:
- No authentication per DC/host
- PSN went down
- System performance
- Replication issues
- AD Connectivity failure issues
- Backup failure
For critical alerts, you might want to configure your environment like the following:
- ISE logs go through the syslog collector and into the Splunk platform.
- The event is converted into an alert with a normalized payload and enriched.
- The alert is sent to a separate Splunk index where alerts from all your Cisco devices go. This is a beneficial step because related alerts from multiple tools can be grouped.
- Action rules based on information in that index determine next steps. This might include:
- Raising a case in ServiceNow
- Sending a notification to a dedicated Webex space
- Notifying other tools integrated in your environment

Informational alert example flow
Informational alerts will vary based on your environment, but some examples are:
- Configuration change report
- Invalid shared keys
- Change of authorization (COA) failure rate report
- Top failing user reports
- Network time protocol (NTP) issues
- Endpoint failure reports
For informational alerts, you can skip the additional Splunk indexing step used for critical alerts and configure the alert to take direct action, possibly sending a notification to a dedicated Webex space or an email inbox.

Real-time ISE traffic analysis, deployment health monitoring, and migration activity tracking
Outcomes of this use case:
- Build and maintain dashboards that provide real-time visibility into ISE traffic, enabling security and operations teams to investigate authentication events and network access issues.
- Track the health status of multiple ISE deployments concurrently, offering a consolidated view of system performance, node availability, and operational metrics across distributed environments to ensure continuous service reliability.
- Monitor major migration activities within ISE deployments or the feature enablement across departments, for example, moving from password-based authentication to certificate-based authentications.
- Provide comprehensive progress updates and clear status indicators for these activities to facilitate smooth transitions, minimize downtime, and enable prompt resolution of any related issues.
- Ensure transparent and effective communication of activity progress to leadership and cross-functional teams, fostering informed decision-making and collaborative oversight throughout the process.
- Support holistic monitoring and management of authentication and security operations across the enterprise.
Dashboards in the Splunk platform reduce time to analyze and visualize data all in one place. The types of dashboards you will create depend on how you use Cisco ISE, but in general, you will want to divide them into operational and management. The following demos show examples of each.
Operational dashboards
Examples of operational dashboards that would be useful for engineers for day-to-day:
- ISE Daily Health Report
- ISE Auth Details
- ISE Anomaly Detection XML
- Check Authentication Status
- MDM Posture Lookup
- ISE EAP Failures
- Endpoint_auth
- VPN user details / UDID Check
- CSIRT and ISE Traffic Flow
- Posture Report Check
- TACACS
Let's look at a demo of an ISE Auth Details dashboard.
Management dashboards
Management dashboards provide quick reporting on how ISE has been performing.
- Enterprise Summary
- Deployment Status
- System Health Check
- Logging Status
- Diskspace Utilization
- User Stats
- Endpoint Stats
Let's look at a demo of an ISE Enterprise Summary dashboard.
Additional resources
Now that you understand the basics of how to use Cisco Identity Services Engine together with the Splunk platform, watch the full talk from Cisco Live EMEA 2026, Revolutionising Cisco IT's Network Operations with Automation, AI and Enhanced Monitoring for more detail and to see a complete demo. You'll also learn about Cisco IT's commitment to advanced network and security operations through strategies to leverage automation, AI, and integrated monitoring for enhanced efficiency and resilience.
In addition, you might find the following resources helpful for achieving this use case:
- Splunk GitHub: Splunk Add-on for Cisco ISE
- Splunkbase: Splunk AI Assistant
- Splunk Help: Welcome to the Search Reference
- Splunk Help: Dashboards overview
- Cisco Identity YouTube: Cisco ISE Integration with Splunk
- Cisco Community: Identity Services Engine and Splunk Apps Configuration Guide