

Setting up a Microsoft 365 abuse mailbox asset in Enterprise Security
When employees report suspected phishing emails, security teams must quickly distinguish genuine threats from spam and false positives. As reporting volumes grow, manual triage can delay the identification of malicious messages and increase the risk of account compromise and data loss.
This article shows you how to install and configure the Microsoft 365 app asset used by Automated Threat Analysis (ATA) in Splunk Enterprise Security to ingest user-reported phishing messages from a Microsoft 365 mailbox through Microsoft Graph. After configuration, messages in the selected mailbox folder are polled and analyzed automatically, with the results surfaced as findings in Splunk Mission Control, so analysts can prioritize credible threats and respond consistently.
Prerequisites
- Splunk Enterprise Security Premier Cloud version 8.5 or later.
- The Automated Threat Analysis module activated in Splunk Enterprise Security Premier. Contact your account team if you are unsure whether Automated Threat Analysis is activated in your environment.
- Permission to install Splunk SOAR apps and configure assets from Splunk Enterprise Security.
- SOAR webhooks activated. The webhook port (3500/tcp by default) must be reachable by Microsoft during the OAuth or admin-consent callback.
- Existing Microsoft 365 mailbox for reported abuse or phishing messages, and known mailbox address and folder to poll.
- One of the following Microsoft Entra roles: Privileged Role Administrator or Global Administrator. This asset requires Microsoft Graph application permissions (see Step 4), and only these roles can grant consent for that permission type. Application Administrator and Cloud Application Administrator can create the app registration but cannot grant this consent.
- A decision on your authentication method: OAuth client secret, Certificate Based Authentication (CBA), or Automatic.
If you have an existing configured asset and are upgrading to a newer app version, select Clone Asset from the asset's three-dot menu. Cloning carries forward the current asset configuration, so you do not need to re-enter credentials or other settings. The cloned asset also exposes the new options available in the updated app version.
Configuration overview
- Install the Microsoft 365 app in Splunk SOAR
- Create the Microsoft Entra app registration
- Configure authentication credentials in Microsoft Entra
- Add Microsoft Graph API permissions in Microsoft Entra
- Configure the Microsoft 365 asset in Enterprise Security
- Configure ingestion settings in Enterprise Security
- Activate the webhook service in Splunk SOAR
- Enable webhooks for the asset in Enterprise Security
- Add the SOAR Route URL to Microsoft Entra
- Run Test Connectivity and complete Microsoft consent in Enterprise Security
- Verify polling and finding creation in Enterprise Security
This process moves between Splunk Enterprise Security, Splunk SOAR, and Microsoft Entra. Keep all three open in separate browser tabs as you work through the steps. You will return to each environment more than once and can pick up exactly where you left off without re-navigating.
Step 1: Install the Microsoft 365 app in Splunk SOAR
- ► Click to expand
-
- Log in to Splunk Enterprise Security and navigate to Configure > Splunk SOAR > Apps.
- Search for the Microsoft 365 app.
- If the app appears, proceed to Step 2.
- If the app does not appear, installation must be completed in Splunk SOAR. Continue with the steps below.
- In Splunk SOAR, navigate to Home > Apps.
- Search for Microsoft 365 in the Configured Apps and Unconfigured Apps tabs.

- If there are no results under either tab, click New Apps.

- Search for Microsoft 365 and click Install.
After installation is complete, the Microsoft 365 asset configuration takes place within Splunk Enterprise Security.
Step 2: Create the Microsoft Entra app registration
- ► Click to expand
-
- Open the Microsoft Entra admin center and confirm that you are in the correct tenant.
- Navigate to Identity > Applications > App registrations and click New registration.
- Enter a descriptive name, such as
Splunk_ES_M365_Abuse_Mailbox. - Select the appropriate Supported account type for your organization.
- Leave Redirect URI blank for now. You will add the SOAR Route URL after the asset is saved in Step 8.
- Click Register.

- After the registration is saved, the app Overview page appears. Copy and store both of the following values; you will need them in Step 5:
- Application (client) ID
- Directory (tenant) ID
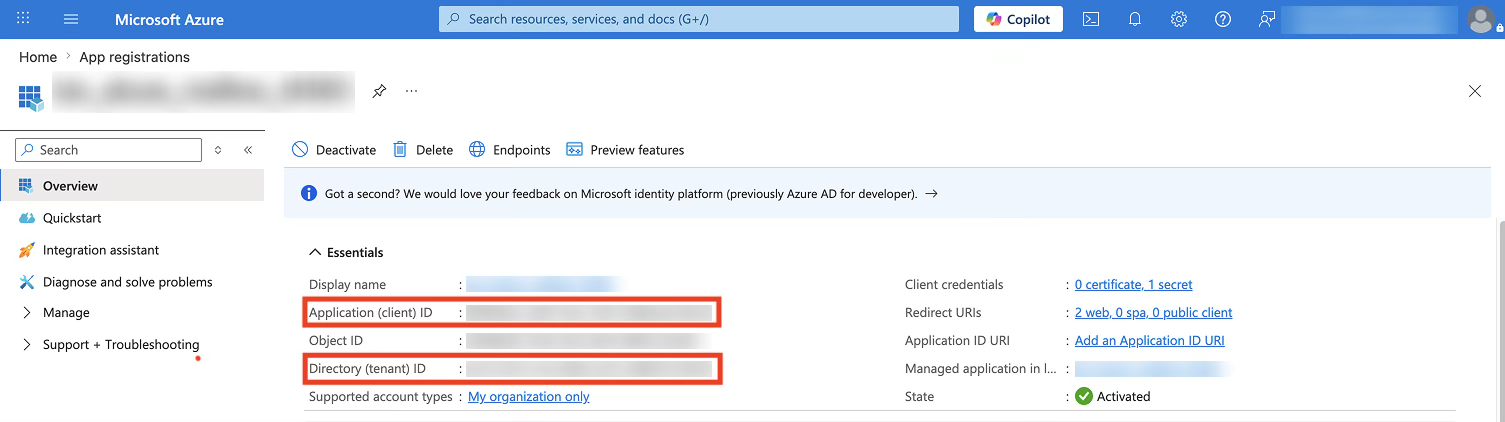
Continue with Step 3 in this tab.
Step 3: Configure authentication credentials in Microsoft Entra
- ► Click to expand
-
OAuth client secret and Certificate Based Authentication (CBA) are both supported. Follow Option A or Option B depending on your chosen authentication method.
Option A: OAuth client secret
- In the app registration, expand Manage > Certificates & secrets.
- Under Client secrets, click New client secret.
- Enter a description and set an expiration period that matches your organization's security policy.
- Click Add.

- Copy the secret Value immediately and store it securely. Microsoft will not show this value again after you leave the page.

Option B: Certificate-based authentication
- Generate or obtain a certificate and matching private key in PEM format, following your organization's certificate standards.
- In the app registration, navigate to Certificates & secrets > Certificates and upload the certificate.

- Copy the certificate Thumbprint and store it for use in Step 5.
When using CBA, you must select Admin Consent Already Provided in the Splunk Enterprise Security asset configuration after Microsoft Graph permissions have been granted in Step 4.
Continue with Step 4 in this tab.
Step 4: Add Microsoft Graph API permissions in Microsoft Entra
- ► Click to expand
-
The permissions you need depend on how you intend to use the asset. Use the table below to identify the least-privilege set for your use case.
Use case Recommended Microsoft Graph application permissions Read and poll abuse mailbox messages User.Read.AllMail.ReadMove, copy, delete, or update messages after analysis User.Read.AllMail.ReadWriteSend messages from Microsoft 365 actions User.Read.AllMail.SendMail.ReadWriteMailbox rules or out-of-office actions MailboxSettings.ReadMailboxSettings.ReadWrite- In the app registration, select API permissions.
- Click Add a permission > Microsoft Graph.

- Select Application permissions and add the permissions for your use case.

- Click Grant admin consent for your organization and confirm the prompt.

Open a new browser tab to continue with Step 5.
Step 5: Configure the Microsoft 365 asset in Enterprise Security
- ► Click to expand
-
- In Splunk Enterprise Security, navigate to Enterprise Security > Mission Control.
- Select Configure > Splunk SOAR from the top menu bar.

- Select Apps.
- Search for Microsoft 365 and click View to access the asset configuration page.

- Click Configure New Asset.

- On Asset Settings, enter the values from the Microsoft Entra app registration and select your authentication method.
Field Value Asset Name A descriptive name, such as m365_abuse_mailboxTenant Directory (tenant) ID from the Entra app Overview page Application ID Application (client) ID from the Entra app Overview page Authentication Type OAuthfor client secret,Certificate Based Authenticationfor CBA, orAutomaticwhen both credential types are configuredApplication Secret Client secret Value from Microsoft Entra. Required for OAuth. Do not use the Secret ID. Certificate Thumbprint Thumbprint from Microsoft Entra. Required for CBA. Certificate Private Key (.PEM) Private key matching the uploaded certificate. Required for CBA. Admin Access Required Keep selected for standard automated email ingestion. Admin Consent Already Provided Leave unselected for the first OAuth Test Connectivity run. Select it after consent succeeds, or when using CBA after consent has already been granted. Access Scope Required only when Admin Access Required is unselected. Enter space-separated Graph scopes. Retry Count / Retry Wait Time Use defaults unless your network or throttling requirements specify otherwise. 
- Stop when you reach Ingest Settings and open a new browser tab to continue with Step 6.
Step 6: Configure ingestion settings in Enterprise Security
- ► Click to expand
-
- Click Next to move to Ingest Settings.
- Use the following table to configure ingestion and finding settings.
Field Value Email Address of the User The mailbox address to monitor, for example abuse@example.comMailbox Folder Folder name, path, or Office 365 folder ID. Use /for nested paths, for exampleInbox/Phishing.Retrieve Folder ID Automatically Keep selected when providing a folder name or path. Clear it only when providing an internal Office 365 folder ID. How to Ingest latest firstfor most new deployments;oldest firstwhen intentionally backfilling older messagesMaximum Containers for First Scheduled Polling Default is 1000. Lower this if the mailbox already contains a large backlog. Maximum Containers for Scheduled Polling Default is 50. Adjust based on expected report volume. Run Threat Analysis Confirm that this is selected. When selected, polled messages are sent to ATA for sandboxing and analysis. Launch automation after threat analysis is complete Confirm that this is selected. When selected, associated Splunk SOAR automation playbooks run after ATA analysis is complete. 
Step 7: Activate the webhook service in Splunk SOAR
This step is only required if you configured OAuth authentication in Step 3. If you used a different authentication type, this step is optional.
- ► Click to expand
-
- In Splunk SOAR, select Administration from the dropdown home menu.
- Navigate to Administrative Settings > Webhook Settings and confirm that webhooks are activated.

Step 8: Enable webhooks for the asset in Enterprise Security
This step is only required if you configured OAuth authentication in Step 3. If you used a different authentication type, this step is optional.
- ► Click to expand
-
- Back in Microsoft 365 asset configuration in Splunk Enterprise Security, click Next to advance to Webhook Settings.
- Select Enable webhooks for this asset.
- Leave Webhooks require SOAR authentication unselected for the Microsoft OAuth callback flow.
- Leave Pass these headers to the webhook handler empty.
- Click Save.
- Copy the generated Route URL. It must end with
/result.Field Value Enable webhooks for this asset Selected Webhooks require SOAR authentication Unselected Pass these headers to the webhook handler Leave empty Route URL Copy the complete URL ending in /result
Step 9: Add the SOAR Route URL to Microsoft Entra
- ► Click to expand
-
- Return to the Microsoft Entra app registration you created in Step 2.
- In the menu on the left, select Authentication (Preview).
- Click Add a platform > Web.

- Paste the SOAR Route URL from Step 8 as the Redirect URI.

- Click Save.
Step 10: Run Test Connectivity and complete Microsoft consent in Enterprise Security
- ► Click to expand
-
- Return to the Microsoft 365 asset in Splunk Enterprise Security.
- Confirm that Admin Consent Already Provided is unselected for the first OAuth run.
- Click Test Connectivity.

- When the test displays the Microsoft authorization URL, open it in a new browser tab while the test is still running.
- Sign in with a Microsoft Entra administrator account that can grant consent.
- Review the requested permissions and click Accept.
- After the browser displays Admin consent received or Authorization successful, return to Splunk Enterprise Security and confirm Test Connectivity Passed.
- Edit the asset and select Admin Consent Already Provided. Save and run Test Connectivity again to confirm that it still passes.
Step 11: Verify polling and finding creation in Enterprise Security
- ► Click to expand
-
- Send a safe test message to the configured abuse mailbox folder.
- Click Poll Now or wait for the configured polling schedule.

- Confirm that the Microsoft 365 asset creates a finding for the test message.
- Open Splunk Mission Control and verify that the finding includes the expected message details and ATA output.
The asset configuration is now complete. The specified abuse mailbox is polled based on the interval or schedule you defined.

Troubleshooting
- If Test Connectivity reports an invalid tenant, confirm that the Tenant field contains the Directory (tenant) ID from the same Entra app registration.
- If Test Connectivity reports an invalid client or application, confirm that Application ID contains the Application (client) ID, not the Object ID.
- If OAuth fails with a secret error, confirm that the asset uses the client secret Value and not the Secret ID. If the value was lost, create a new client secret.
- If Microsoft rejects the redirect, confirm that the Entra Web redirect URI exactly matches the SOAR Route URL, including host, port, path, asset identifier, and trailing
/result. - If admin consent times out, run Test Connectivity again and complete the Microsoft consent page while the test is still waiting.
- If permission errors appear, verify that Microsoft Graph application permissions were added and admin consent was granted for the tenant.
- If CBA fails, confirm that Certificate Thumbprint and Certificate Private Key (.PEM) match the uploaded certificate and Admin Consent Already Provided is selected.
- If polling succeeds but no emails are ingested, verify Email Address of the User, Mailbox Folder, Retrieve Folder ID Automatically, and the first-run polling limits.
- If folder lookup fails, verify that the folder name is correct (it is case-sensitive), nested paths use
/, and the asset is not treating a folder ID as a folder name. - If the webhook callback never reaches Splunk SOAR, confirm that the SOAR base URL and webhook port are reachable. For FedRAMP or on-premises deployments, confirm the required network path before retrying.
Next steps
You might find the following resources useful for implementing the guidance in this article:
- Splunk Lantern Article: Setting up a Google Workspace abuse mailbox asset in Splunk Enterprise Security